FIPS 140-2 Compliant
Encrypted End-to-End
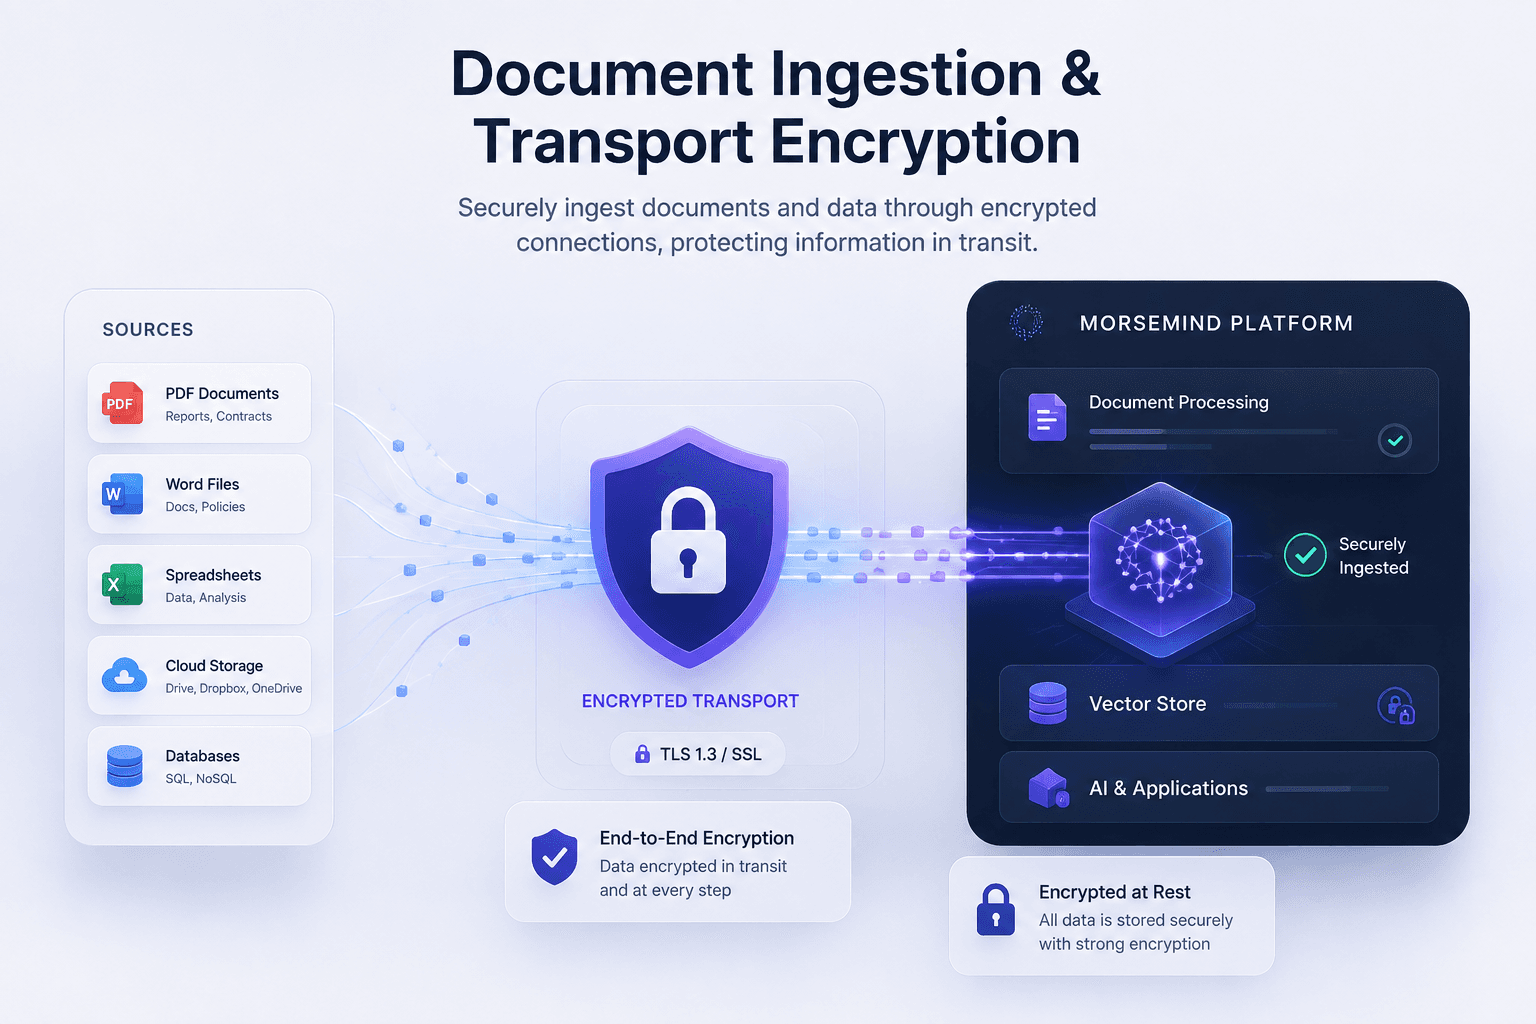
Documents, vector embeddings, and conversation histories are encrypted with AES-256 at rest and TLS 1.3 in transit.
Bank-grade AES-256 encryption, strict tenant isolation, and zero public model training. Deploy enterprise retrieval-augmented generation without compromising data ownership or regulatory compliance.
Protection at Every Layer
Every layer of MorseMind is designed to keep your business data private, verifiable, and protected against unauthorized access.
Documents, vector embeddings, and conversation histories are encrypted with AES-256 at rest and TLS 1.3 in transit.
Your proprietary knowledge is never fed into external public LLM training datasets. What's yours stays yours.
Answers are grounded strictly in approved corporate context, featuring full source citations for review.
Seamless SAML 2.0 / Okta / Azure AD authentication paired with document-level role-based access control.
Multi-tenant vector databases feature strict cryptographic namespace separation and tenant key isolation.
Detailed exportable audit streams tracking every query, retrieval event, and access permission update.
Interactive Architecture Flow
Click through each phase of our enterprise RAG pipeline to explore the security controls operating at every step.
Data uploaded to MorseMind is transmitted over encrypted TLS 1.3 channels. Raw documents are parsed in ephemeral memory workers, split into chunks, and encrypted with tenant-unique AES-256 keys prior to vectorization.
Control Matrix & Governance
Inspect our technical controls, cryptographic standards, and compliance mappings in detail.
| Control Name | Technical Specification | Compliance Standard | Status |
|---|---|---|---|
Data at Rest Encryption Data Encryption | AES-256 GCM cryptographic encryption for document chunks, vector databases, and Postgres metadata. | SOC 2 CC6.1 / FIPS 140-2 | Enforced |
Data in Transit Encryption Data Encryption | Strict TLS 1.3 encryption with HSTS enforcement for all REST, GraphQL, and WebSocket endpoints. | ISO 27001 A.10.1 | Enforced |
Single Sign-On (SSO) Access & Identity | SAML 2.0 and OpenID Connect (OIDC) integration supporting Okta, Azure AD, Ping Identity, and Google Workspace. | SOC 2 CC6.2 | Active |
Role-Based Access Control (RBAC) Access & Identity | Granular document collection, bot workspace, and admin user role permissions (Admin, Editor, Viewer). | ISO 27001 A.9.4 | Enforced |
Zero Data Training Policy AI & Model Safety | Contractual and technical isolation ensuring customer queries and vector chunks are never logged for public model training. | GDPR Art 28 / SOC 2 | Enforced |
Prompt Injection & Jailbreak Guard AI & Model Safety | Automated input guardrails sanitizing user queries before passing into vector retrieval context. | OWASP Top 10 for LLMs | Enforced |
Immutable Audit Trails Infrastructure & Audit | Exportable SIEM event stream capturing user logins, vector searches, permission changes, and API key generation. | SOC 2 CC7.2 | Configurable |
Dedicated VPC & Private Deployment Infrastructure & Audit | Optional single-tenant deployment in AWS, Azure, or GCP with dedicated VPC peering and private endpoints. | Enterprise Single-Tenant | Active |
Frequently Asked Questions
Common questions from IT security officers, compliance teams, and enterprise architects.
Ready when you are
Build an assistant your customers and teams can rely on, grounded in the knowledge you already own.